Technology Due Diligence for UK SMEs: What to Check Before an Acquisition, Investment or Major
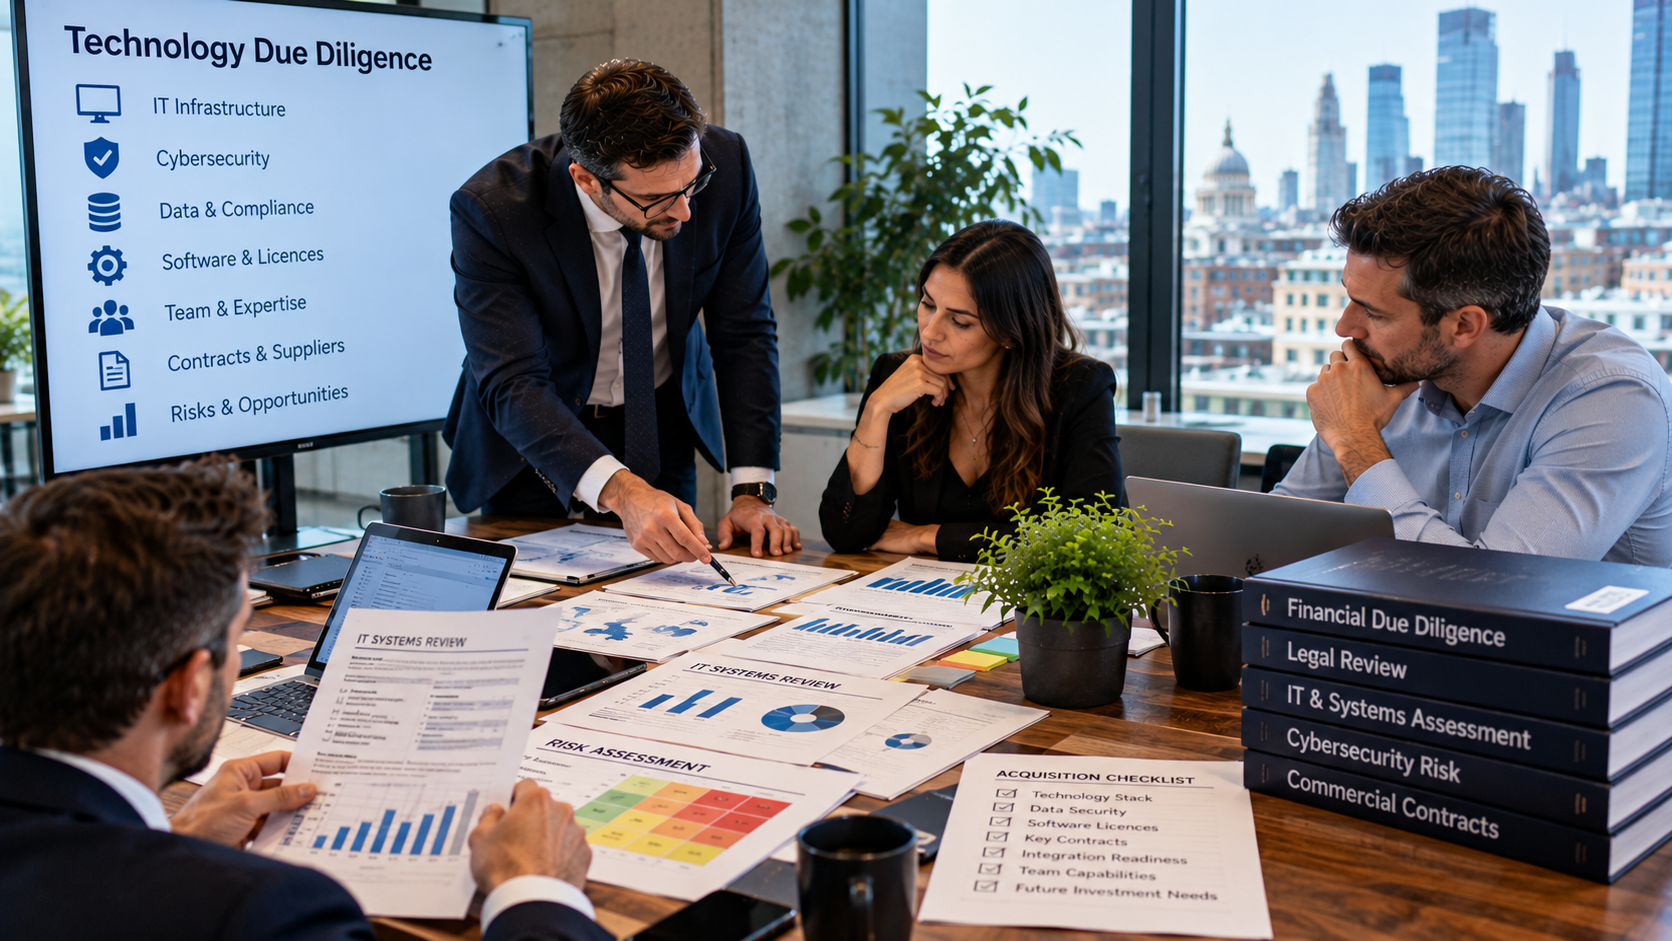
Business Change
Technology Due Diligence for UK SMEs | Nexteck
Discover how UK SMEs can assess software, cybersecurity, data, IT costs and system dependencies before an acquisition, investment or major business change.
technology due diligence for UK SMEs
IT due diligence UK, technology risk assessment, software due diligence, digital due diligence, IT systems audit, business acquisition technology checklist, cybersecurity due diligence, technology integration planning, IT infrastructure assessment, technology investment risk
London and the wider United Kingdom; SME owners, company directors, investors, acquisition teams, professional services firms, manufacturing businesses and growing companies.
Informational and commercial investigation; aimed at businesses preparing for investment, acquisition, restructuring or significant technology expenditure.
Introduction: A business can look healthy while its technology hides expensive risks
When a company prepares for an acquisition, investment, merger, ownership transition or major expansion, attention often focuses on revenue, customers, profitability and market position. These are important measures, but they do not always reveal the full condition of the business.
Behind the financial figures, the organisation may depend on outdated software, undocumented integrations, spreadsheets maintained by one employee, inconsistent customer records or technology contracts that are difficult to exit. It may also have security weaknesses, unclear ownership of its digital assets or operational processes that cannot support a larger customer base.
These issues can affect the cost, timing and complexity of a business transaction.
Technology due diligence is the structured assessment of a company's technology environment, systems, data, contracts, risks and future investment requirements. It helps decision-makers understand what they are taking on, which weaknesses need attention and whether the technology can support the business plan.
For UK SMEs, this assessment does not always need to resemble a large enterprise audit. The appropriate scope depends on the organisation's size, industry, transaction value, regulatory exposure and dependence on technology.
A small professional services firm with a handful of cloud applications will have different requirements from a manufacturer operating production systems, an e-commerce company processing substantial customer data or a fintech business handling sensitive financial information.
The common objective is to replace assumptions with evidence before committing to a consequential business decision.
What is technology due diligence?
Technology due diligence examines the systems and technology-related obligations that influence a company's ability to operate, grow and manage risk.
Depending on the circumstances, it can cover:
Software applications, licences and subscriptions.
IT infrastructure, hosting and cloud services.
Cybersecurity controls and incident history.
Data quality, access, ownership and portability.
System integrations and technical dependencies.
Custom software, source code and intellectual property.
Supplier contracts, renewal dates and exit conditions.
Technology team capabilities and key-person dependencies.
Business continuity, backups and disaster recovery.
Future investment required to support growth.
The findings should connect technology conditions to commercial implications. A list of applications is not enough; decision-makers need to understand what each important system does, what happens if it fails, how much it costs and whether the business can change or replace it.
A structured review of Nexteck's industry solutions can also help frame technology questions around the company's operating sector, rather than relying on a generic checklist alone.
Why technology due diligence matters for UK SMEs
1. It helps reveal costs that are not obvious in headline financial figures
A company may report manageable monthly IT expenditure while depending on a collection of subscriptions, specialist support agreements, integrations and manual workarounds.
Some costs are easy to identify, such as software licences and hosting. Others are less visible: employees correcting duplicate records, consultants maintaining an undocumented system, or staff spending hours preparing reports that should be automated.
A due diligence review should distinguish between current expenditure, future commitments and potential remediation costs.
For example, a business may need to upgrade unsupported software, replace a system that cannot scale, improve backup arrangements or consolidate overlapping tools. These requirements may affect the investment needed after a transaction.
Avoid assuming that every identified weakness requires an expensive replacement. Some issues may be addressed through configuration, documentation, training or integration.
2. It identifies operational dependencies
A business may rely on one application for orders, another for finance and a third for customer records. If these systems are connected through manual exports or undocumented scripts, the process may be fragile.
The risk becomes more significant when the business is expanding or changing ownership. New reporting requirements, additional users or integration with another company's systems may expose limitations that were previously manageable.
A technology assessment should identify:
Which systems are essential to daily operations.
How information moves between applications.
What happens if a critical supplier becomes unavailable.
Whether another person can maintain the system.
Whether the business can recover data after an incident.
Which processes rely on undocumented workarounds.
This information helps decision-makers understand whether the technology environment can support the proposed business plan.
3. It clarifies cybersecurity and data protection exposure
Security weaknesses can create operational, financial and reputational consequences. Due diligence should assess the controls relevant to the business, its data and its operating environment.
Questions may include whether multifactor authentication is enabled, whether access permissions are appropriate, how backups are protected, whether security updates are applied and whether incidents have been recorded and handled.
For businesses processing personal data, the review should also examine relevant UK data protection responsibilities, supplier arrangements, retention practices and access to sensitive information.
The exact legal and regulatory requirements depend on the circumstances. A technology review should not be treated as a substitute for specialist legal, regulatory or cybersecurity advice where that is necessary.
4. It tests whether the technology supports future growth
Systems that work for a small team may become difficult to manage when the organisation adds employees, customers, locations or product lines.
For example, a business might depend on manual stock updates across several sales channels. Increasing order volume could create more reconciliation work and increase the likelihood of errors.
Similarly, a professional services firm might manage projects through separate spreadsheets, email and finance tools. Growth could make it harder to track capacity, project profitability and outstanding invoices consistently.
The review should therefore consider not only whether technology works today, but also whether it can reasonably support the business's expected growth.
5. It helps prioritise investment after the transaction
Not every weakness needs immediate remediation. Some issues create urgent operational or security risks, while others are opportunities to improve efficiency over time.
A prioritised technology plan can separate:
Immediate risks that require prompt attention.
Essential improvements needed for continuity.
Integration work needed to support the transaction.
Efficiency opportunities that can be delivered later.
Longer-term investments linked to the growth strategy.
Nexteck's main website outlines its broader approach to technology strategy, systems improvement and custom software. The underlying principle is to connect technology decisions to business outcomes rather than treating every technical issue as equally important.
A practical technology due diligence checklist
The following framework can help UK SME owners and decision-makers organise an initial review. It is a starting point, not a formal certification or a replacement for specialist due diligence.
1. Build an inventory of critical systems
List the software, platforms, infrastructure and services that support important business activities.
For each system, record its purpose, business owner, supplier, approximate cost, renewal date, data stored, integrations and operational importance.
Flag applications that are unsupported, poorly documented or understood by only one employee.
Key question: If this system became unavailable tomorrow, which business activities would stop or become significantly harder?
2. Review software contracts and licence conditions
Technology contracts can influence the cost and feasibility of a transaction.
Check renewal periods, termination provisions, minimum commitments, user-based pricing, data export options, service levels and any restrictions on transferring or changing the service.
Where the transaction involves a change of ownership, verify whether the relevant agreements require consent or contain change-of-control provisions. The precise implications should be reviewed by an appropriately qualified legal adviser.
Also confirm that software is properly licensed and that the business has sufficient evidence of its rights to use and maintain important applications.
3. Assess cybersecurity and resilience
Review the controls that protect systems and help the business recover when something goes wrong.
Depending on the organisation, relevant areas may include:
User authentication and privileged access.
Security updates and endpoint protection.
Backup coverage and restoration testing.
Incident response procedures.
Supplier access and third-party risk.
Business continuity arrangements.
Security monitoring and incident records.
A backup policy is not the same as a proven recovery capability. Where possible, examine evidence that restoration procedures have been tested and that recovery objectives are realistic.
For a more complex or sensitive environment, an independent technical assessment may be appropriate.
4. Examine data quality and ownership
Data can be a valuable business asset, but its usefulness depends on accuracy, accessibility and appropriate control.
Check whether customer records are duplicated, whether key information is missing, whether reporting definitions are consistent and whether employees can identify the authoritative record for important data.
Review who can access the data, where it is stored, how long it is retained and how it can be exported or transferred when a supplier relationship ends.
For custom-built applications, clarify who owns the relevant intellectual property, what rights are granted under development agreements and whether the business has access to the source code and documentation it needs.
5. Map integrations and technical dependencies
Identify how the main applications exchange information.
A simple diagram can show where customer, order, financial, inventory and reporting data originate and how they move between systems.
Document any integration that depends on manual file transfers, individual employee knowledge, custom scripts or third-party services.
For each critical connection, consider what happens when the integration fails, how errors are detected and whether the process can be restored without reconstructing information manually.
6. Evaluate team capability and documentation
Technology risk is not limited to software and hardware.
A business may depend heavily on one employee or external contractor who understands how a critical application works. If that person becomes unavailable, the organisation may struggle to maintain the system or resolve incidents.
Review technical documentation, administrator access, support arrangements, operating procedures and knowledge-transfer plans.
This is particularly important where an acquisition combines teams, changes responsibilities or requires a different support model.
7. Estimate remediation and integration costs
Translate identified problems into realistic work packages.
For each issue, estimate the effort, cost range, dependencies, business impact and implementation risk. Distinguish confirmed requirements from assumptions that need further investigation.
Possible cost categories include:
Cost category | Questions to investigate |
|---|---|
Software and licences | Are subscriptions duplicated or due for renewal? |
Infrastructure | Will hosting or equipment need an upgrade? |
Security | Are additional controls or independent testing required? |
Integration | Must systems be connected or migrated? |
Data | Is cleaning, reconciliation or migration necessary? |
People | Is training or specialist support required? |
Continuity | Are backup, recovery or documentation gaps present? |
Modernisation | Is unsupported software creating a material risk? |
Avoid presenting speculative savings as guaranteed returns. A credible assessment should show the assumptions behind its estimates and explain what additional evidence is needed.
8. Create a prioritised action plan
The final output should be more than a long list of technical findings.
A useful action plan identifies each issue, its business consequence, the recommended response, an accountable owner, an indicative cost and a target timeframe.
A simple prioritisation model can assess two dimensions:
Impact: How seriously could the issue affect customers, operations, finances, security or the transaction?
Urgency: How quickly must the business act to reduce the risk or enable the planned change?
High-impact, time-sensitive issues should receive attention first. Lower-priority improvements can be scheduled according to available resources and the wider business strategy.
The Nexteck SME Strategy & Tracking Toolkit provides a relevant place to explore structured diagnostic, opportunity-planning and KPI-governance approaches that can support ongoing technology decision-making.
Technology due diligence before an acquisition or merger
An acquisition introduces additional considerations because the business may need to operate within a new technology environment.
Before completion or integration, the parties should establish which systems must continue operating, which data needs to be transferred, what access is required and which contracts or supplier relationships may need attention.
Common integration questions include:
Can the two organisations exchange customer and financial information reliably?
Are their identity, access and security arrangements compatible?
Which system will become the authoritative source for shared data?
Will employees need new licences or access permissions?
Are there contractual restrictions on transferring services?
Which applications should remain separate during the transition?
What is the fallback plan if a migration is delayed?
A phased integration is often more manageable than attempting to replace every system at once. Critical operations should be protected, and migrations should have defined testing, approval and recovery procedures.
For regulated or highly technical environments, independent specialists may need to assess additional legal, operational or sector-specific obligations.
Technology due diligence before external investment
Investors and lenders may need confidence that the business's technology can support the proposed commercial plan.
The most useful evidence is usually specific and verifiable. It may include a system inventory, a documented technology roadmap, software cost information, security policies, backup test records, architecture diagrams and a clear explanation of major technical dependencies.
A growing company should also be able to explain how its technology supports revenue, customer service, operational efficiency and scalability.
For example, if the business plan assumes a substantial increase in order volume, the technology review should investigate whether the current systems can support that increase or whether additional investment will be required.
The aim is not to claim that technology is risk-free. It is to demonstrate that material risks are understood, prioritised and addressed through a credible plan.
When should a UK SME seek specialist support?
An initial internal review may be sufficient for a straightforward business with limited technology dependencies. Specialist support becomes more valuable when the transaction is complex, systems are poorly documented or the consequences of failure are significant.
Consider additional expertise when:
The company relies on bespoke or legacy applications.
Sensitive personal or financial information is involved.
There is uncertainty over software ownership or licensing.
Multiple systems must be integrated.
The business has experienced security incidents.
Technology remediation could materially affect the transaction.
Management needs an independent assessment of the technology roadmap.
A good review should remain proportionate to the business. It should explain the evidence, distinguish material risks from minor issues and produce recommendations that management can realistically implement.
Turning due diligence findings into business value
The value of technology due diligence comes from what the business does with the findings.
A well-organised assessment can support better investment decisions, improve continuity planning, clarify supplier commitments and help management allocate technology budgets more effectively.
It can also reveal opportunities to simplify systems, improve reporting or redesign processes that have become difficult to manage.
The next step is to turn the findings into a staged improvement plan, with owners, costs, priorities and measurable outcomes.
For businesses that need a structured view of their systems and future technology requirements, the Nexteck website is a starting point for exploring its business technology advisory approach. The aim should be a technology environment that supports the business plan without introducing unnecessary complexity or cost.
Conclusion: Understand the technology before committing to the business decision
Technology due diligence helps UK SMEs look beyond headline financial performance and understand the systems, contracts, data and operational dependencies that support the business.
Whether a company is preparing for an acquisition, seeking investment, entering a new market or planning a major transformation, the review should identify material risks, estimate the work required to address them and connect recommendations to commercial priorities.
Start with an inventory of critical systems, verify the most important contracts and controls, investigate dependencies, and document the cost and urgency of each material issue.
Considering an acquisition, investment or major technology change? A structured assessment can help clarify the risks and identify the improvements that matter most. Explore Nexteck's services to understand its industry-focused technology and operational approach.
Frequently asked questions
What is technology due diligence?
Technology due diligence is a structured assessment of a business's software, infrastructure, data, cybersecurity, supplier contracts, technical dependencies and future technology requirements. It helps decision-makers understand material risks and investment needs.
Why is IT due diligence important when buying a business?
It can identify unsupported systems, unexpected technology costs, security weaknesses, software ownership questions and integration challenges that may affect the transaction or the business's future operations.
What does an IT due diligence checklist include?
A practical checklist typically covers critical systems, software licences, supplier contracts, cybersecurity, data quality, backups, integrations, technical documentation, team capability and the cost of required improvements.
How long does technology due diligence take?
The timeframe depends on the size and complexity of the business, the quality of its documentation, the number of systems involved and the depth of the review. A simple assessment may be relatively short, while a complex transaction can require detailed technical investigation.
Does technology due diligence include cybersecurity?
Yes, cybersecurity is commonly an important part of the assessment. The depth of review depends on the business's risk profile and may include access controls, patching, backups, incident history, supplier access and recovery arrangements.
Who should carry out technology due diligence?
The review may involve internal IT staff, independent technology consultants, cybersecurity specialists, software experts and legal advisers. The appropriate team depends on the transaction and the risks being assessed.
Is technology due diligence only necessary for large companies?
No. SMEs can also have critical technology dependencies, software contracts and data risks. The review should be proportionate to the size, complexity and importance of the proposed business decision.
What happens after the technology due diligence report?
Management should prioritise the findings, assign owners, estimate costs, agree deadlines and track progress. Urgent risks should be addressed promptly, while longer-term improvements can be incorporated into the business's technology roadmap.